Websites, client portals, mobile apps, booking systems, and payment pages often sit between a business and its customers. That position makes them valuable targets for attackers. A single compromised account can expose customer information, enable fraudulent transactions, or give an intruder a path into connected systems. Businesses should therefore treat customer-facing platforms as critical infrastructure rather than simply another marketing or service channel.
Make Account Access Harder to Exploit
Passwords remain a common weak point. Customers may reuse credentials across multiple sites, allowing attackers to test passwords stolen elsewhere against a company’s platform. Rate limiting, compromised-password screening, and multi-factor authentication can reduce this risk.
Administrative accounts deserve stricter controls. Employees with access to customer records, payment settings, or system configurations should use multi-factor authentication and individual accounts rather than shared credentials.
Permissions should also reflect job responsibilities. A customer service employee who needs to view an order should not automatically have permission to export an entire customer database.
Monitor What Happens After Login
A successful login does not prove that the legitimate account owner is behind it. Stolen credentials can allow attackers to enter through the same login page customers use every day.
Monitoring should therefore extend beyond failed login attempts. A sudden password change followed by a large download, repeated changes to payment information, or an unusual volume of transactions can signal account takeover.
Payment integrations deserve similar attention. Businesses using platforms such as ClickSWITCH or other services that connect financial information and digital workflows should know what data moves between systems, which permissions are granted, and how access can be revoked. The goal is to recognize unusual behavior early enough for someone to investigate it.
Reduce the Data Available to Steal
Businesses often collect customer information simply because a form or software platform makes it possible. Every additional piece of stored information creates another asset that must be protected.
Review forms, account profiles, and databases periodically. If information has no current business purpose, consider whether it needs to be collected or retained.
Sensitive data that must remain should have appropriate access restrictions and encryption. Retention policies can also establish when old records should be securely deleted instead of remaining indefinitely in forgotten databases or cloud accounts.
Do Not Forget Third-Party Connections
Customer-facing platforms rarely operate independently. A website might connect with a CRM, payment processor, scheduling platform, analytics service, email system, and several plugins.
Each connection can introduce additional exposure. Businesses should maintain an inventory of integrations and remove those that are no longer used. API keys, administrator accounts, and application permissions should receive the same attention.
Software updates matter too. Outdated plugins and libraries can leave known vulnerabilities available to attackers even if the visible website appears to function normally.
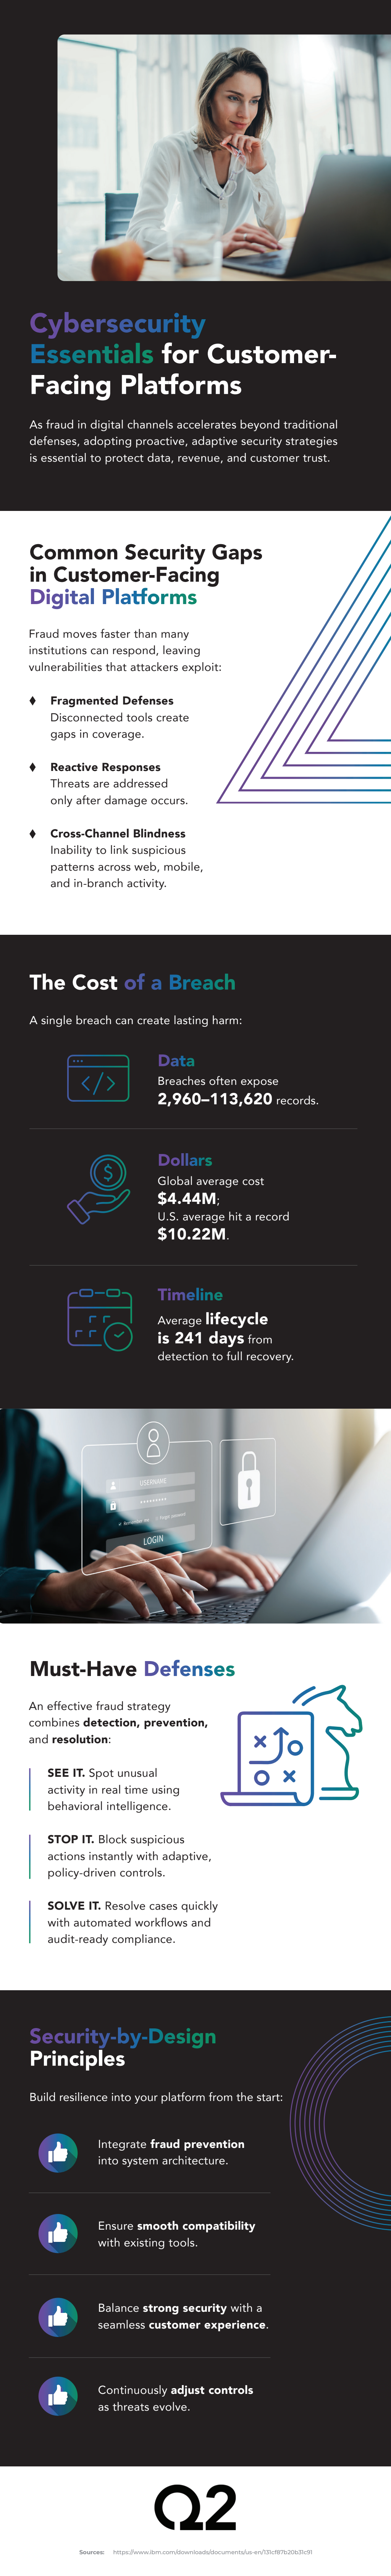
Customer-facing security depends on layers. Strong authentication can reduce account compromise, monitoring can expose suspicious behavior, and careful data practices can limit what an attacker can reach. Regular reviews of third-party access, software updates, backups, and response procedures strengthen those layers. Look over the infographic below to learn more.